“How does it look like?” is the question. Not having or not marketing it is out of question! Why have it? Well, let’s answer that right now; why not when we can have it! What goes in there? Summarily everything that’s not part of the regular CV. And elaborately? Well, what do you think this blogpost is about?
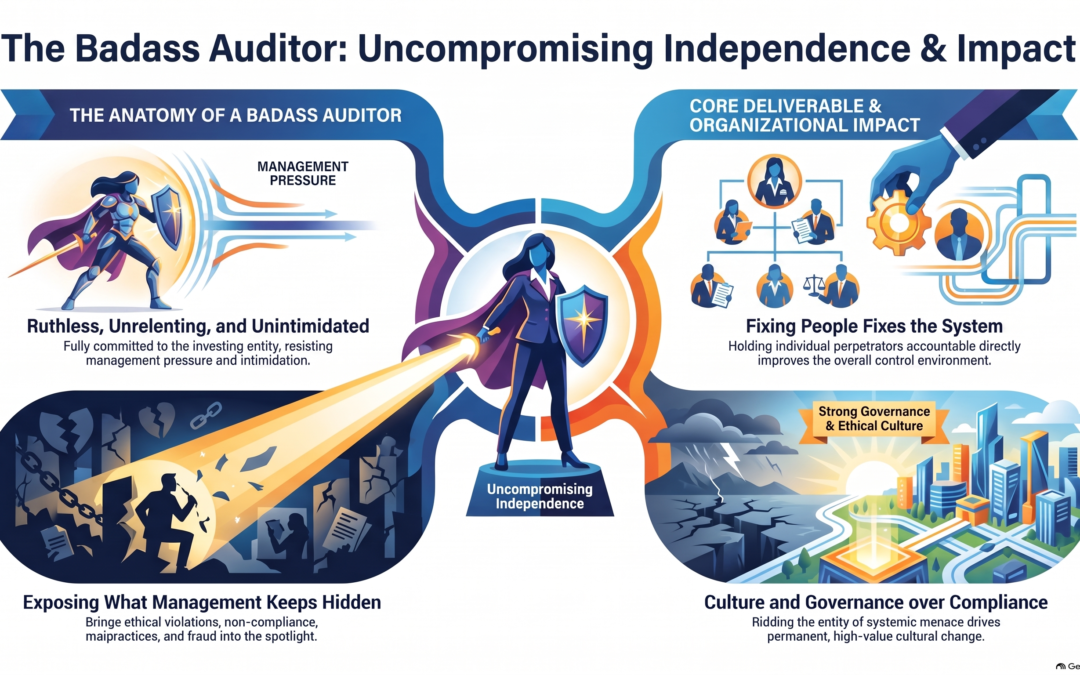
Definitions first! A bad@ss auditor is the ruthless, unrelenting and unforgiving kind of a professional internal auditor. Internal Auditor because external ones scope is limited. Ruthless because this internal auditor cannot be influenced or intimidated. So, this auditor can’t be expected to go with the flow, management’s flow!
This auditor is fully loyal and committed to only one thing: the entity investing in it. And the auditor efforts are worth every penny invested. Naturally therefore, management stuff that reeks of ethical violations, non-compliances, control violations, malpractices, fraudulent conduct, etc. get the limelight they deserve, courtesy the auditor’s efforts!
And that’s when the auditor becomes bad@ss, essentially an adversary to the management’s efforts to have its way through its means based on its motivations. Yeah!, you got that right, means and motivations to do the things they were neither appointed for nor entrusted with! And we do understand how means and motivations wear out the ethical principles!
So, the bad@ass auditor gets this kind of reputation owing to those bad exposures brought to the fore thanks to its efforts. Exposures the entity is left reeling from, due to mismanagement that was intended to remain hidden and even those for which genuine efforts were made to sweep these under the carpet! Resultantly, not just the strategic, financial, operational, compliance and reporting exposures get reported, but the culprits also get exposed.
In fact, the culprits, the perpetrators getting not just the exposure that they asked for, but also the comeuppance (only sometimes unfortunately!) is the key deliverable from an auditor’s perspective. And this should also be the core deliverable and solution from the management and the Board’s perspective too!
Because a perpetrator caused something contrary to the interests of the entity either willfully by exploiting vulnerability or deliberate bypassing of controls or using ignorance as an excuse. The thing is that if the managements and the Boards are serious in fixing a system after such an incident, they need to fix the person first. Because fixing that person fixes the control environment and by acting against such a person, Boards especially can say out loud and clear that governance is not something to be messed with!
Enough said. Let’s get to the bad@ss CV we desire to explore here! Let me be an example!
|
#* |
Year** |
Casualty |
Action |
By |
On Account Of*** |
|
1 |
2010 |
Head of Operations |
Fired |
Board |
Multiple policies violations |
|
2 |
2012 |
Regional & Branch Manager Sales |
Fired |
Management & Board |
Sales & AR Fraud |
|
3 |
2012 |
Assistant Manager Logistics |
Fired |
Management |
Inventory Fraud |
|
4 |
2013 |
CSD Technicians (multiple) |
Fired |
Management |
Cash Fraud |
|
5 |
2013-14 |
CSD Accountants (multiple) |
Fired |
Management |
Cash & Inventory Fraud |
|
6 |
2018 |
HR Compensations Executive |
Transferred & Incentive Withheld |
Management |
Misuse of Authority, Records manipulation |
|
7 |
2019 |
Assistant Manager Medical |
Fired |
Management |
Fake credentials |
|
8 |
2022 |
Manager Operations |
Warning & Incentives Withheld |
Management |
Control violations, ethical misconduct |
|
9 |
2025 |
Manager HSE |
Demoted |
Board Audit Committee |
Forged & Fabricated records, ethical misconduct |
|
10 |
2025 |
Financial Controller |
Warning |
Board Audit Committee |
Incompetence, Multiple procedural non-compliances |
|
11 |
2026 |
CEO |
Forced to Resign |
Board |
Incompetence, Demonizing controls, Ethical Misconduct, Promoting recognized offenders, Control Violations, Derogatory behavior towards Internal Audit |
*some entries missed because management took alternate actions as offences were not serious in nature and exposure and alternate actions brought desired improvements
**gap years represent job and scope transitions
***based on irrefutable evidence
One can always find ways to improve this CV further. For instance, wherever possible, exposures in numbers could be added, though ethical violations are priceless! Color coding could be used to distinctly identify different categories of offences. One may briefly identify the nature of engagements and audit approaches that led to these findings Classifications could be used for instance from amongst GRC domains or internal controls frameworks! And more.
But one doesn’t need to log the benefits of these actions! To rid the entity of such menace is self-explanatory! Though recording improvements in systems made to plug in the gaps aimed at preventing recurrence are a good idea!
And since these are bigger accomplishments owing to the control environment or cultural change they bring, it might as well be a good idea to list these alongside those other accomplishments in a regular CV!
It’s not that we choose to fight these battles. Falling out with us is entirely the management’s choice! We’re made to fight these because we insist upon staying true to our identity, our independence and objectivity!
I have always ventured in a new territory with an open mind hoping to find integrity and professionalism. But the eerie similarities of the turf every time faded those hopes out and raged the fires I carry!
And well, I’ve been consistent in my approach and have persevered through abject, absolute, acute and chronic friction! In fact, that friction always kept me going.
And it was usually like, the violations finding me, rather than me actively in pursuit of them!
It’s important to be on the right side of the audit when your auditor is bad@ss!
Yeah bad@ss auditors are bad news!